
IBM Warns Fewer Than 10% of Organisations Are Prepared for Quantum Computing Threats
IBM executive Alessandro Curioni says fewer than 10% of organisations worldwide are prepared for quantum-related cybersecurity risks, warning that future quantum computers could undermine encryption protecting financial systems, digital communications and sensitive information.

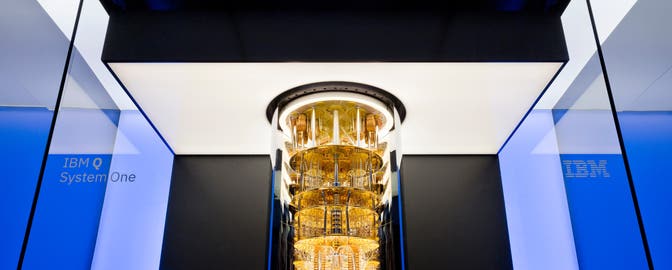
IBM has warned that most organisations worldwide remain unprepared for the cybersecurity risks that could emerge as quantum computing advances. Alessandro Curioni, IBM’s vice-president for Europe and Africa and head of IBM Research in Zurich, told Agence France-Presse on October 14 that fewer than 10% of organisations had become “quantum-safe.” His comments, reported on October 15, highlight growing concerns that future quantum computers could eventually compromise some of the cryptographic systems currently used to protect confidential information. Quantum computing is an emerging field that uses principles of quantum physics to process information in ways that differ from conventional computers. Although the technology could support scientific breakthroughs and complex calculations, it may also introduce significant security challenges as its capabilities improve.
The central concern is that sufficiently powerful, fault-tolerant quantum computers could break certain widely used public-key encryption systems. These cryptographic methods help secure online transactions, digital signatures, confidential communications and other essential digital services. Conventional computers would require impractical amounts of time to solve some of the mathematical problems underlying these systems, but a sufficiently capable quantum computer running an appropriate algorithm could potentially solve them much more efficiently. Such machines do not currently have the demonstrated capability to break modern encryption at a large scale. However, security experts are encouraging organisations to begin preparing now because upgrading complex digital infrastructure can take years, particularly when systems depend on older software, external suppliers and long-lived confidential data.
Another concern is known as “harvest now, decrypt later.” In this scenario, attackers collect encrypted information today and store it until future technology might allow them to decrypt it. This could threaten sensitive government communications, financial records, corporate intellectual property and personal information that must remain confidential for many years. Information does not need to be immediately readable to have future value to an attacker. Organisations that handle long-term confidential data therefore face pressure to assess which information would be most damaging if exposed and how long it needs to remain protected. Curioni’s warning reflects the growing view among cybersecurity specialists that quantum readiness should be treated as a present-day planning responsibility rather than a problem to address only when powerful quantum machines become available.
IBM is among the companies working to develop practical quantum computing systems. The company aims to deliver a large-scale, fault-tolerant quantum computer for commercial clients by 2029, according to its current roadmap. Fault tolerance is important because quantum systems are vulnerable to errors that can undermine calculations; practical machines will need reliable methods to detect and correct those errors. At the same time, governments and cybersecurity organisations are developing strategies for transitioning to post-quantum cryptography, which uses mathematical methods designed to resist attacks from both conventional and quantum computers. The United Kingdom’s National Cyber Security Centre has set out a transition roadmap extending to 2035, encouraging organisations to identify vulnerable systems, prioritise critical information and plan upgrades.
The warning also highlights the potential benefits and risks of quantum technology. Researchers are investigating its possible applications in drug discovery, materials science, optimisation and the simulation of complex physical systems. IBM and other technology companies are investing heavily in research, hardware development and software tools in the hope of making these applications commercially useful. However, the security implications mean that progress must be accompanied by preparation across the public and private sectors. Organisations can begin by inventorying their cryptographic systems, identifying data that requires long-term protection, consulting security specialists and developing migration plans for quantum-resistant algorithms. Although the precise timeline for a machine capable of breaking widely used encryption remains uncertain, experts argue that early preparation will reduce the cost and disruption of future upgrades. IBM’s latest warning reinforces the message that quantum computing is both a promising scientific development and a challenge that cybersecurity planning cannot afford to ignore.




