French Cybersecurity Agency Reports Copeland Refrigeration Systems Hacked
France’s cybersecurity agency says refrigeration systems associated with Copeland and its subsidiary Dixell were compromised in a cyberattack that disrupted supermarket operations, spoiled food and raised concerns about the security of connected industrial equipment.

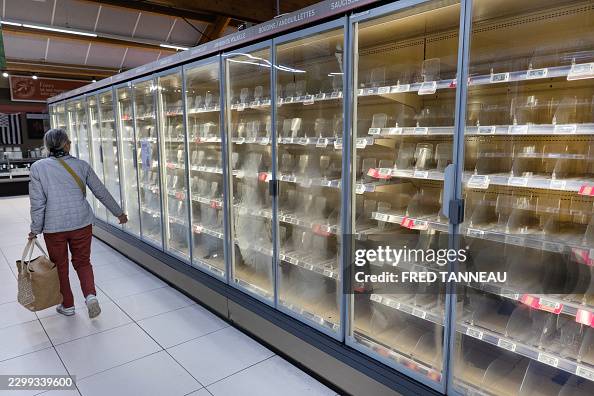
France is investigating a major cyberattack that targeted refrigeration systems in supermarkets across the country, with authorities reporting that equipment associated with Copeland and its subsidiary Dixell was also affected. On October 13, 2026, France’s national cybersecurity agency said the incident involved compromised refrigeration control systems used to manage temperatures in commercial refrigerators and freezers. The attackers reportedly manipulated the systems, causing temperatures to rise dramatically and threatening the safety of stored food. The incident affected multiple supermarket operators and highlighted how cyberattacks against seemingly ordinary equipment can disrupt essential services. Investigators are continuing to examine how the systems were accessed and whether the same vulnerabilities could be exploited elsewhere.
The attack reportedly caused refrigeration temperatures to climb as high as 50 degrees Celsius in some locations, resulting in spoiled fresh and frozen products. Several supermarkets were forced to discard food, while reports also described fires at some affected stores. Reuters reported that at least 350 supermarkets were caught up in the incident, including outlets associated with Carrefour, Monoprix, Intermarché and Coopérative U. France’s finance minister said approximately 700 supermarkets had been affected, illustrating the scale of the disruption as authorities assessed the consequences. The incident also created additional work for retailers, which had to inspect equipment, restore safe operating conditions and replenish damaged stock.
The involvement of Copeland and Dixell has drawn attention to cybersecurity weaknesses in connected industrial equipment. These systems use electronic controllers and software to monitor temperatures and regulate refrigeration performance. Although they are primarily designed to maintain safe storage conditions, remote connectivity can introduce security risks when devices are improperly configured, exposed directly to the internet or running outdated software. France’s cybersecurity agency said systems associated with Danish manufacturer Danfoss were also affected. Investigators are examining whether attackers exploited known vulnerabilities or weaknesses in the way the equipment was connected to remote management services. Copeland did not independently confirm all details of the reported compromise but said protecting customers’ operations was its priority and that it was working with affected customers to mitigate risks.
The incident has raised concerns because refrigeration equipment plays an important role in food distribution and public safety. Supermarkets rely on controlled temperatures to preserve meat, dairy products, frozen foods and other perishable goods. When refrigeration systems fail or are deliberately manipulated, businesses may face substantial financial losses, while food that has been exposed to unsafe temperatures may need to be discarded. Cybersecurity specialists have warned that older industrial devices can remain vulnerable when manufacturers no longer provide security updates or operators fail to replace unsupported equipment. The French incident demonstrates that cybersecurity is not limited to computers, smartphones and financial systems; connected machinery in retail stores, factories, hospitals and other essential facilities can also become a target.
France’s cybersecurity agency has advised affected operators to take precautions before reconnecting refrigeration equipment to the internet, including using secure network connections, installing available firmware updates and changing passwords. Businesses are also being encouraged to review remote-access permissions, isolate operational technology from ordinary office networks and replace unsupported systems where necessary. Investigators had not identified a publicly confirmed perpetrator, and no group had claimed responsibility in the Reuters reporting. The absence of a clear motive means it remains uncertain whether the attack was intended to cause disruption, exploit vulnerable devices or achieve another objective. The investigation is ongoing, while the incident has renewed calls for stronger security standards for industrial equipment and better protection of the digital systems that support food supply chains.