
Amazon Warns Hackers Exploited Critical PHP Vulnerabilities Before Public Disclosure
Amazon says attackers began targeting two critical PHP security flaws four days before their public disclosure, highlighting how AI-assisted hacking is accelerating cyber threats and reducing the time organisations have to protect vulnerable systems.

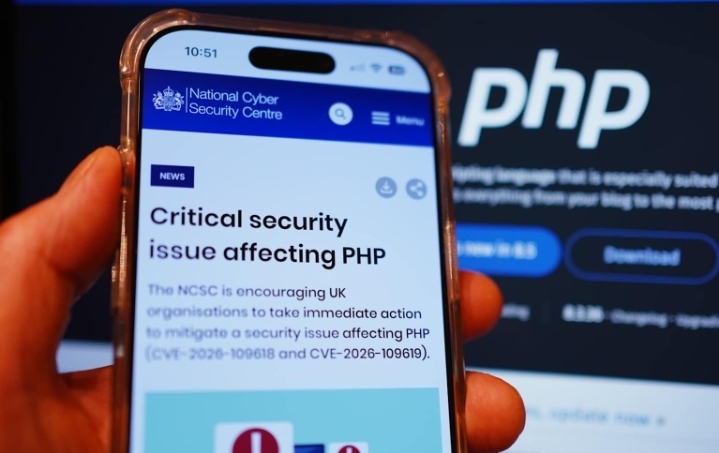
- Amazon has warned that cybercriminals attempted to exploit critical vulnerabilities in PHP, a widely used programming language that powers millions of websites and online applications, before the security flaws were publicly disclosed. In a security report published on October 21, 2026, Amazon Threat Intelligence said its monitoring systems detected suspicious activity targeting the vulnerabilities on October 17, four days before the official disclosure and release of security patches. The vulnerabilities, collectively referred to as PHP2Shell, were tracked as CVE-2026-109618 and CVE-2026-109619. According to Amazon Web Services (AWS), the first identified attempt originated from an internet address associated with a commercial anonymisation network. Investigators said it remains unclear how the attacker obtained information about the vulnerabilities before the coordinated disclosure.
The vulnerabilities are particularly dangerous because they can allow attackers to execute malicious code remotely on affected servers without first authenticating themselves. This type of weakness, known as remote code execution, can potentially give an attacker a pathway to interfere with a website, access sensitive information or establish further control over a compromised system. The PHP security team released emergency fixes on October 21, urging administrators to update affected installations immediately. Both vulnerabilities received a critical severity rating of 9.2 under the CVSS 4.0 scoring system. Amazon said that, following public disclosure, it observed multiple attempts to exploit the flaws using different infrastructure and attack payloads. The variation suggested that several threat actors were attempting to take advantage of the vulnerabilities, although Amazon cautioned that it had not established whether every observed attempt would have succeeded against real-world systems.
Amazon’s findings also revealed how quickly exploitation activity increased once technical details became public. The company reported observing proof-of-concept exploits within hours of the disclosure, followed by additional attempts against its monitoring infrastructure. Security researchers use honeypots such as Amazon’s MadPot network to attract suspicious activity and study the methods attackers use. These systems can provide early warnings about emerging threats before organisations have completed their own investigations. Amazon said the incident demonstrates why companies should not assume that a vulnerability becomes dangerous only after its official announcement. In this case, the earliest identified exploitation attempt preceded public disclosure by four days, leaving organisations potentially exposed before they had an opportunity to install the available patches.
A major concern raised by the incident is the growing role of artificial intelligence in cybersecurity attacks. Amazon warned that AI-assisted analysis can make it easier for attackers to study security patches, understand the weaknesses they address and develop working exploits. Previously, less-skilled attackers often depended on experienced researchers to publish ready-made exploitation tools before launching their own attacks. That delay is becoming less reliable as AI tools help more people analyse technical information and adapt existing techniques. Separate reporting has described a surge in attempts to exploit the PHP2Shell vulnerabilities following disclosure, with security organisations observing activity against exposed systems worldwide. However, the available evidence does not establish that AI was responsible for the specific attack observed on October 17. The incident instead illustrates the wider challenge of defending software when vulnerabilities can be exploited rapidly and, in some cases, before public disclosure.
Amazon has urged organisations running vulnerable PHP installations to prioritise security updates, investigate suspicious activity and reduce exposure while patching systems. The company recommends checking server logs for unusual requests, looking for suspicious use of the PHP_SESSION_UPLOAD_PROGRESS field in multipart file uploads, and investigating unexpected process execution or file modifications. Administrators who cannot immediately install the updates may consider temporary protective measures, including blocking certain upload requests where applications do not require them. However, AWS stresses that such measures are not a complete substitute for installing fixed PHP versions. The company also recommends investigating activity dating back to at least October 17 rather than limiting security reviews to the date the vulnerabilities were publicly disclosed. The warning reinforces the importance of rapid patching, continuous monitoring and effective incident-response procedures as cyber threats continue to evolve.




