
PHP Warns of Third Security Flaw Amid Growing Cybersecurity Crisis
PHP developers have disclosed a third remote-code-execution vulnerability following two critical security flaws that triggered emergency updates and disrupted websites worldwide, renewing concerns about the security of internet infrastructure and the growing role of artificial intelligence in cyberattacks.

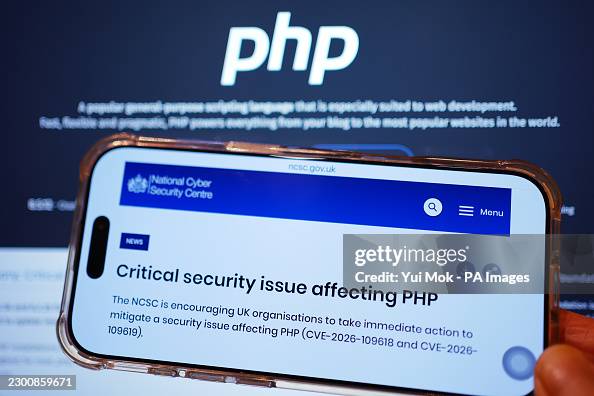
The developers behind PHP, one of the world’s most widely used programming languages for website development, have warned of a third security vulnerability amid an ongoing effort to protect internet-facing systems. The latest flaw, identified as CVE-2026-115560, was disclosed on October 23, 2026, shortly after emergency updates were released to address two earlier critical vulnerabilities. According to the European Union’s cybersecurity agency, CERT-EU, the new issue could potentially allow remote code execution under a specific combination of application and configuration settings. However, PHP’s security team considers that configuration uncommon and has not announced an emergency software release for the third flaw. The disclosure adds another complication for organisations already working to identify vulnerable systems and apply security updates.
The third vulnerability follows two serious flaws, CVE-2026-109618 and CVE-2026-109619, which security researchers collectively refer to as PHP2Shell. Both vulnerabilities were rated 9.2 out of 10 under the Common Vulnerability Scoring System and could allow unauthenticated attackers to execute malicious code on affected servers. The problems involve weaknesses in PHP’s handling of memory and internal request data when certain errors occur. Because the vulnerabilities affect the PHP runtime itself, rather than only individual websites or applications, a wide range of services could be exposed. PHP is used by major content-management platforms, including WordPress, Drupal and Joomla, meaning that organisations must assess their underlying server software even if their websites appear to be functioning normally.
The impact of the earlier vulnerabilities has already extended beyond individual technology companies. Reuters reported that government websites and other online services were taken offline as administrators worked to protect their systems following the disclosure of the critical flaws. Some organisations temporarily disabled services as a precaution while testing and applying fixes. Security researchers also warned that attackers could study the released patches to develop techniques targeting systems that remained unprotected. Although reports of exploitation attempts have emerged, the extent of successful attacks remains uncertain. CERT-EU has urged organisations to install the available security updates immediately and consider isolating internet-facing applications if they cannot be patched promptly.
The incident has also drawn attention to the growing role of artificial intelligence in discovering and exploiting software vulnerabilities. Researchers at cybersecurity company Wiz reportedly used AI models and their Atlas platform to help identify weaknesses, investigate their underlying causes and validate possible exploit techniques. IBM reported that AI-assisted analysis helped researchers complete work that could previously have taken months in a much shorter period. While these capabilities can strengthen defensive security by helping developers identify flaws more quickly, the same acceleration could benefit malicious actors searching for unpatched systems. The PHP incident therefore illustrates the dual-use nature of AI in cybersecurity: it can improve vulnerability detection and remediation, but it can also shorten the time available for organisations to protect themselves after a weakness becomes known.
For organisations using PHP, security experts recommend identifying all affected installations, applying the appropriate vendor-provided updates and checking for signs of compromise where exposure may have occurred. The fixed releases for the two earlier critical vulnerabilities include PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. The third vulnerability has a narrower reported configuration requirement, and the PHP security team recommends disabling session.upload_progress.enabled and restarting affected workers as a temporary mitigation until a regular bug-fix release becomes available. Such configuration changes should be implemented by qualified administrators, as temporary measures are not a substitute for installing official security updates. The latest warning reinforces the importance of regular software maintenance, rapid vulnerability assessment and effective monitoring as AI continues to reshape the cybersecurity landscape.




