
Citizen Lab Exposes Israeli Ad-Tech Firm Accused of Enabling Zero-Click Spyware Attacks
Researchers say Israeli advertising company Discover-Tech exploited online advertising networks to track internet users and help deliver spyware without requiring victims to click links, raising serious concerns about digital privacy and global cybersecurity.

A major investigation by the University of Toronto’s Citizen Lab and advertising security company Confiant has uncovered an alleged surveillance operation that used ordinary online advertisements to help infect devices with spyware. Published on October 15, 2026, the investigation identified an Israeli advertising technology company called Discover-Tech as a link between commercial advertising platforms and companies involved in developing surveillance software. Researchers said the company’s advertising infrastructure could identify, profile and target internet users, with certain advertisements reportedly used to deliver malicious code to selected devices. The technique, described as “AdFection,” demonstrates how systems designed to deliver personalised advertisements can potentially be repurposed for espionage. Unlike conventional cyberattacks that depend on victims opening suspicious links or downloading infected files, this method can reportedly compromise a targeted device simply by displaying a specially prepared advertisement.
According to the investigation, Discover-Tech operated advertising platforms that connected it to major digital advertising networks, allowing its advertisements to appear across websites and mobile applications. Researchers reported that the company’s advertisements reached more than 120,000 websites and approximately 75,000 applications through various partnerships. Its advertising activity reportedly involved billions of bidding requests within a period of several months in 2026. The advertisements often resembled ordinary promotions for consumer products, making them difficult for users to distinguish from legitimate advertising. Researchers said the company could collect advertising identifiers and other technical information, including IP addresses, to help identify devices and determine whether particular users matched the profiles selected for surveillance. The findings raise questions about how much information the online advertising industry can collect and whether existing safeguards are sufficient to prevent legitimate advertising infrastructure from being exploited for covert monitoring.
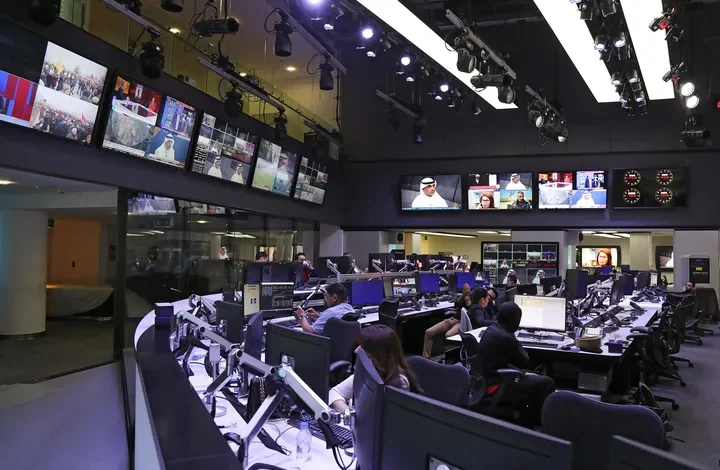
One of the investigation’s most serious findings concerned the alleged use of Discover-Tech’s infrastructure to deliver spyware developed by Candiru, an Israeli surveillance software company previously blacklisted by the United States government. Citizen Lab said it found evidence that at least 45 devices associated with Al Jazeera were targeted and infected with Candiru spyware during 2024 and 2025. The investigation followed concerns raised by the broadcaster’s own technical team, which had identified suspicious activity on devices used by some journalists. According to the researchers, the spyware could potentially access sensitive information stored on compromised devices. However, the investigation did not identify the government or specific client that ordered the operation against Al Jazeera. Researchers also found advertisements associated with Discover-Tech appearing across networks used by government bodies, international organisations and technology companies, although the appearance of an advertisement alone does not establish that a device was infected.
The revelations have prompted several companies and industry organisations to take action against Discover-Tech. Google said it had terminated the company’s access to its advertising platforms following the investigation, while IAB Europe removed it from its approved vendor listings pending further scrutiny. Other advertising providers also suspended or blocked the company’s accounts and domains. These measures highlight the difficulty of monitoring large-scale advertising systems in which advertisements are bought and sold through automated auctions involving numerous intermediaries. Researchers said malicious advertising campaigns could evade routine security checks by delivering different content depending on a viewer’s device, location or IP address. This selective behaviour can make it difficult for automated scanners to detect dangerous advertisements because the malicious code may only appear when a particular target views the advert.
The investigation has renewed calls for stronger regulation and security standards across the digital advertising industry. Citizen Lab warned that the same infrastructure used to profile consumers for commercial purposes could be exploited to target journalists, activists, government officials and other individuals of interest to surveillance operators. Cybersecurity specialists recommend that users, particularly those at elevated risk of targeted attacks, use reputable security software, keep operating systems and applications updated, consider content-blocking tools and limit unnecessary advertising-tracking permissions. These precautions can reduce some risks but cannot guarantee protection against sophisticated spyware. The findings also underline the importance of independent investigations, transparent advertising practices and stronger cooperation between technology companies and security researchers. Although the full scope of Discover-Tech’s alleged activities remains uncertain, the case demonstrates how systems built for online marketing can create serious security risks when exploited for covert surveillance.




